What Secure Occupational Health Software Needs
Short answer
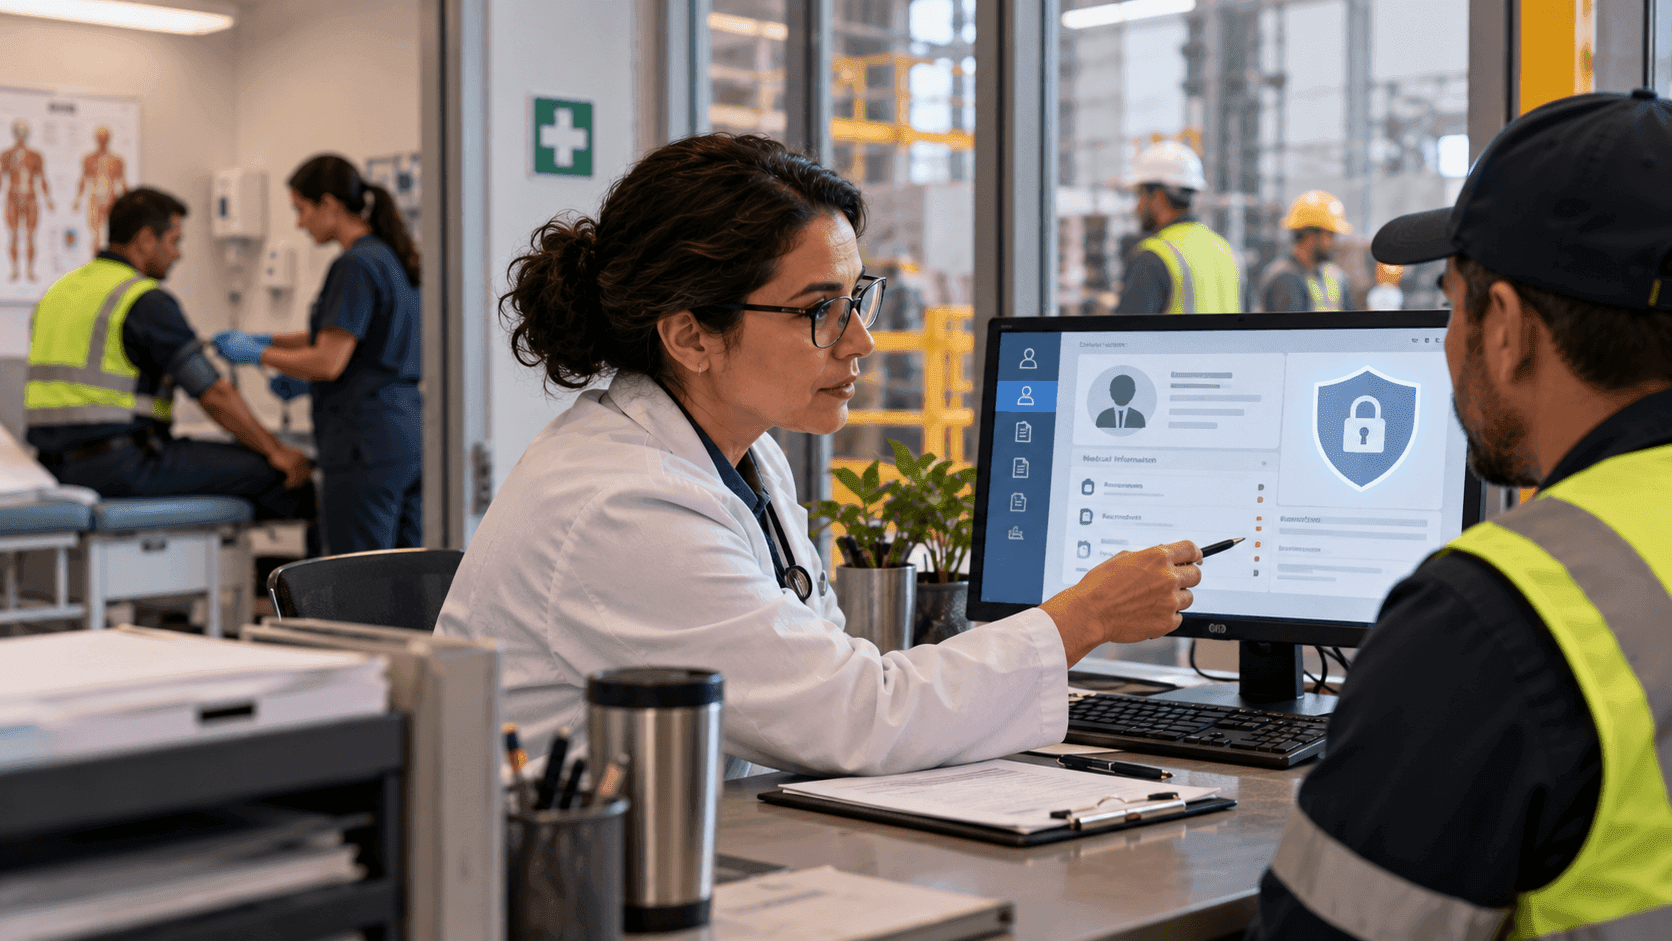
Occupational health software should protect employee clinical data by design: least-privilege access, clear separation of clinical and operational information, encryption, audit trails, retention controls, and a deployment model that fits the organization’s regulatory obligations. A feature list without governance is not enough.
- Role-based, least-privilege access
Users should see only what they need for their defined responsibility. Occupational-health professionals may require clinical detail; managers may only require fitness-for-work or restrictions status; EHS teams may need aggregated risk signals. Permissions should be reviewable and revocable.
- An auditable record of access and change
The system should record who viewed, created, changed, exported, or approved sensitive information, and when. An audit trail supports investigations, compliance reviews, and accountability.
- Separation between health and operations
The platform should distinguish confidential clinical records from operational workflow data. This makes it possible to support safe work, accommodations, and compliance without exposing medical detail to people who do not need it.
- Encryption and secure integration
Evaluate encryption in transit and at rest, identity integration, secure backups, and controls for data exchange with clinics, HR systems, insurers, or EHS platforms. Ask how integrations enforce permissions and whether data is duplicated unnecessarily.
- Retention, deletion, and data residency
Requirements vary by jurisdiction and record type. The software should support documented retention schedules, lawful deletion or archival, and the appropriate deployment or hosting model. Regulated organizations may require private or self-hosted options.
- Governance over AI features
If the platform uses AI, require transparent boundaries: what data is available to the model, whether it is used for training, what actions are allowed, how results are validated, and when human review is required.
Nova Sentinel is designed around governed employee-health history, EHS risk context, auditability, and controlled access. Talk to an expert
FAQ
Is encryption enough to protect employee health data?
No. Encryption is essential, but access control, auditability, process design, retention, and user governance are equally important.
Should managers have access to health records?
Only to the minimum operational information they legitimately need, subject to applicable law and organizational policy.
When is private deployment worth considering?
Consider it when regulatory, contractual, data-residency, or security requirements cannot be met by the proposed shared environment.
Stay ahead in your industry
Subscribe and receive curated content about what's happening in your industry and news that can impact your business. No spam, just the good stuff!